Frontier AI access is a location problem.
Congress wants AI chips to prove where they are, but the models only get an IP lookup.
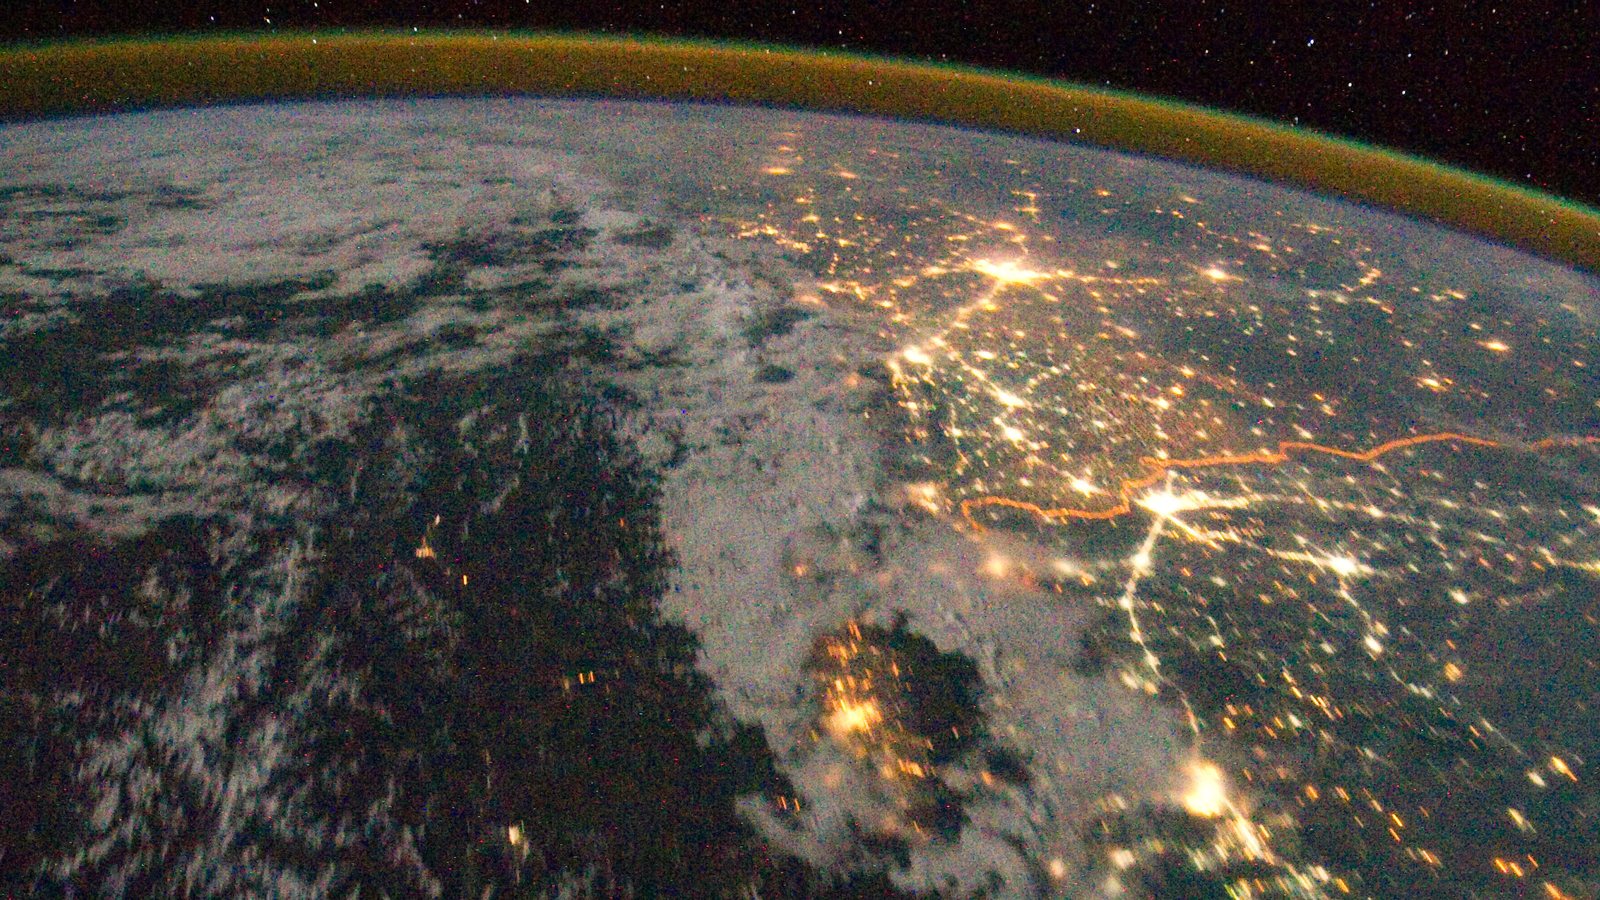
NASA, ISS028-E-29679. Public domain.
Every person on the internet is somewhere: in a room, in a city, in a country. The internet doesn't record where. A website sees only an IP address, and a VPN lets anyone choose where that address appears to be. Even without a VPN, an IP address is an estimate. Cloudflare documentation: “There is nothing that inherently binds an IP address to a physical location or country.”
The United States controls which countries its most sensitive hardware and information can reach. Weapons, their parts and advanced chips need approval to be sent abroad, and Congress can block major arms sales. Know-how is controlled too. Emailing controlled chip designs to China can require a license, and so can showing them to a Chinese engineer in an office in California.
Frontier AI models are restricted on the same grounds. Anthropic does not offer Claude in China “for national security reasons.” A buyer in Shenzhen can still reach it through a transfer station, a reseller that forwards requests from a server outside China, for 70–90% less than the official price and without a VPN.
In March, the House Foreign Affairs Committee voted 42–0 to advance the Chip Security Act. It requires advanced AI chips (the 3A090 and 4A090 classifications: Nvidia's H100 and everything comparable) to be “secured by a chip security mechanism that enables reliable verification of whether the product has been illegally diverted to destinations of concern.” Location verification is one of the mechanisms it names.
Congress looked at a national-security problem and decided the buyer's word was not enough. The chip itself has to be able to show where it went.
The models those chips train and run are still gated by IP address. Six billion people are online, and one in five web sessions now arrives through a VPN. And the share is higher wherever location decides access. For example, when the UK required age checks in July 2025, Proton VPN's UK sign-ups rose 1,400% within hours, and Ofcom counted daily VPN app users doubling to 1.5 million.1
80,000 relays
This month, the security firm Team Cymru counted relay servers: machines that pass requests to US AI models on someone else's behalf. An eight-day scan found 10,867 of them. They ran on 457 different networks, and no single hosting company ran more than about 11% of them, so shutting down one company would not shut them down. Since then, Team Cymru has found more than 80,000 relay servers.
The relay runs in a country the AI company serves, and it holds the account. The AI company sees the relay's location and the relay's account. It does not see the person typing, who may be somewhere the company refuses to serve. Scott Fisher, who wrote Team Cymru's report: “Account attribution, usage metering, rate limits, abuse detection, regional availability, and the terms that govern all of them are enforced against whoever holds the credentials.”
In China these relays are called transfer stations. Writing for ChinaTalk in May, Zilan Qian explained that a transfer station “accepts API requests, forwards them as if they originated from the transfer station's location, and passes the response back.” Tokens sell for about 1 RMB per dollar of usage, “70–90% below official prices,” paid through WeChat or Alipay. The buyer needs no VPN and no foreign card.
In one cluster, Team Cymru found over 4,000 IP addresses from China and Hong Kong connecting in. Over eight days, that traffic came to 14 TB uploaded and 7 TB downloaded. Seventeen relay servers pushed 81 GB into Anthropic and pulled back 1.4 GB of responses.
Anthropic described the same machinery in February. The proxy services reselling Claude to Chinese labs run what it calls “hydra cluster” architectures: “sprawling networks of fraudulent accounts.” A single proxy network managed more than 20,000 of them at once. “When one account is banned, a new one takes its place.”
OpenAI told Congress that DeepSeek was getting around its restrictions
On 12 February, OpenAI sent a memo to the House Select Committee on the Chinese Communist Party. “We have observed accounts associated with DeepSeek employees developing methods to circumvent OpenAI's access restrictions and access models through obfuscated third-party routers and other ways that mask their source,” it said. “DeepSeek employees developed code to access US AI models and obtain outputs for distillation in programmatic ways.” And: “Chinese companies rely on networks of unauthorized resellers of OpenAI's services to evade our platform's controls.”
The mechanism is not in dispute, nor is it new. The company whose models were targeted described it to Congress seven months ago, in writing. Researchers have now measured it at scale.
What the labs do today
The obvious reply is that nobody relies on an IP address alone. Both major labs have layered real identity controls on top, and those controls are not trivial.
OpenAI requires organization verification for access to frontier models in the API: legal business name as it appears in official records, registered address, a tax or business registration identifier, current official business documents, and an unexpired physical government-issued ID from a supported country. One individual can verify only one account or organization, and attempting more can get you blocked. That rule exists because OpenAI knows about resale. Its memorandum to Congress described a resale network.
Anthropic added an ownership test. In September 2025, it began prohibiting access by entities more than 50% owned, directly or indirectly, by companies headquartered in unsupported regions, wherever the entity itself operates. Its reasoning: companies subject to control from authoritarian jurisdictions face legal requirements that can compel them to share data or cooperate with intelligence services, and they can't easily resist that pressure wherever they're incorporated. Firms in restricted regions had been setting up subsidiaries in permitted ones to get access. In April 2026, Anthropic also began requiring select users to verify with a government-issued photo ID and a live selfie.
The transfer station supply chain has an answer for each of these checks. ChinaTalk lists accounts registered in bulk, SMS platforms that sell foreign phone numbers, and tools that generate fake IDs. All of these checks run once, at sign-up. What the gray market sells is an account that has already passed them.
Commerce has required a license for API access to a model
In June 2026, Commerce did something it had never done before. Acting under the Export Control Reform Act and section 744.22(b) of the EAR, it treated an AI model itself as controlled technology (not the weights, not the source code, the model), and it treated remote, API-based access to that model as a “release” requiring a license.
Commerce had consistently held that remote access to cloud-hosted software is not an export. The directive named specific models and was lifted within weeks. But the legal theory is now on the record: giving a foreign person API access to a controlled model can be an export.
The same directive reached “any foreign person worldwide (including if employed by Anthropic in the United States).” That is deemed-export doctrine applied to model access. The question is not only who connects from outside. It is also who inside the building can reach what.
If the theory is applied again, the geographic control on a frontier model is no longer a business policy. It is an export control. Under export controls, a company can be penalized even if it tried in good faith to keep restricted users out.
Regulators have already ruled on this exact control
Crypto exchanges faced it first.
In 2023, Binance agreed to pay $4.3 billion to settle with US authorities, including $968 million to OFAC. OFAC found that Binance's IP address screening “allowed for a user to change their IP address using a Virtual Private Network (VPN) and access trading services even after failing Binance's KYC screening.” It also found that Binance “continued to allow trades by users who were logged in from an IP address in a comprehensively sanctioned jurisdiction so long as that user had submitted KYC documents from a non-sanctioned jurisdiction.”
A year earlier, OFAC had penalized Bittrex roughly $24 million, citing, among other failures, that it did not screen IP address or physical address information to identify customers in sanctioned jurisdictions. In its 2022 settlement with Payward, Kraken's parent company, OFAC named as an aggravating factor that Kraken “applied its geolocation controls only at the time of onboarding and not with respect to subsequent transactional activity.”
A location check at sign-up is not enough. It has to hold for each transaction.
That is the gap in the labs' controls. The frontier labs run identity checks at enrollment. Even the strongest identity check answers a different question. A passport and a live selfie prove who opened the account. They say nothing about where that person is when a request is sent, or whether that person is the one sending it. What runs afterward watches behavior, not position. A regulator has already found that posture deficient in an adjacent industry, attached penalties to it, and put in writing what it expected instead.
The controls work after the fact
Anthropic published its threat intelligence report on 10 September. It covers operations disrupted between December 2025 and August 2026. Again and again, the actor was in a region Anthropic does not serve and got in anyway.
Iranian state propaganda units: “Access to Claude from within Iran is blocked, so they used VPNs and foreign phone numbers to register and verify accounts.” A Russia-based team building drone software routed its traffic through commercial virtual private servers. A procurement operation buying dual-use goods for Russian defense customers used VPNs, and the report adds: “Like those in other cases in this report, this actor used VPNs to circumvent Anthropic's geographic access restrictions.”
A reseller platform serving users in unsupported regions “tunneled traffic through US infrastructure to evade our regional blocks.” Anthropic banned the accounts and took down the relays. “The operator re-established access within days.”
Seven China-based labs ran distillation campaigns through transfer stations, which, in Anthropic's words, “create thousands of new accounts using false identities, fake or stolen credit cards, and stolen API keys.” One pool attributed to Alibaba ran nearly 5,000 accounts on residential proxies. Anthropic counted over 151 million exchanges from Alibaba between May and July 2026. The same proxy networks carried traffic from DeepSeek and Xiaomi.
Anthropic found these operations and banned the accounts. In the Iranian case, it learned where the actors were because they named their locations in conversation. By then the actors had defeated every check made at sign-up: IP address, phone number, identity and card. The ban comes after the model has done the work, and ChinaTalk reports that “the upstream supply chain can easily set up a new proxy within hours.”
Move the question from the credential to the device
A relay works for one reason: the provider trusts whoever holds the key. Everything downstream of that trust (the country check, the rate limit, the tier) is enforced against a credential, and a credential can be sold.
Stop asking the credential where it is. Ask the device.
A device produces a signed statement about its own position. It is either the device making the request or an enrolled phone bound to it. The position is measured on that device from its own sensors, not inferred from the network path. The signature is made by a key held in the secure element, which software on the device cannot reach or extract. The platform vendor attests that the hardware is genuine, the operating system is not rooted or jailbroken, and the code that produced the result is the code the developer published. Apple's App Attest and Google's Play Integrity already do that last part, at scale.
Now a server in Virginia cannot answer for a person in Hangzhou. The answer has to come from a device bound to the request, signed by hardware that the device cannot lie about. Routing becomes irrelevant. The packets can take any path they like.
This is not a novel arrangement. Apple Pay has kept a device-specific account number inside the secure element since 2014, and the payments industry has relied on that boundary at global scale for over a decade. It is also what the Chip Security Act asks of the chip: a mechanism on the device that can show where it has gone. The argument here is only that the model deserves the same treatment as the card that pays for access to it.
What we built
Octet is a proof of location protocol. The device measures its own position with its own sensors, evaluates a policy question (is this device inside or outside a defined region?) and returns a signed yes or no. Coordinates never leave the device. Anyone can verify the result offline with an open-source verifier that doesn't depend on us, so a regulator or a counterparty can check it without trusting the company that ran the check or the vendor that built it.
Both of our SDKs are in production: one runs inside mobile apps, the other in the browser.
- Mobile SDK. In an installed app, it resolves country and US state with no location permission and no prompt to the user. With location permission, it proves the device is at a specific place: for example, that a site inspection photo was taken on site.
- Browser SDK, by request. It resolves a visitor's country with nothing asked of the visitor: no permission prompt and no account. A VPN does not defeat it. Country is the determination that export controls and sanctions turn on.
Octet enables geofactor authentication: location, proven by the device, used as a factor in an access decision. Location Factor Authentication (LFA) is one form of it, built for sign-in. It works the way a passkey or a one-time code from a 2FA app does. A website or an API issues a location challenge, the enrolled phone answers it, and the relying party receives a signed verdict on the region and nothing else. Because the phone answers, LFA works for requests from machines with no location sensors of their own, such as a laptop or a server calling an API. The measurement does not have to happen on the machine making the request. It has to be bound to it. The challenge can also repeat throughout a session, so location is checked while the account is in use, not only when it signs in. That is the check OFAC faulted Kraken for lacking.
Geofactor authentication for frontier models
Congress decided that an exported chip must be able to show where it has gone, rather than rely on what the buyer declares. That judgment is correct.
But a control is defeated at its cheapest point, not at its strongest. Getting H100s into China means evading export controls and moving hardware worth millions of dollars across a border, where it can be seized. From China, using a model trained and running on those same chips takes a transfer station account.
The models sit behind a check that any relay gets around, and Commerce has told the companies that build them that giving a foreign person access can be an export. If location is worth proving in hardware for the chip, it is worth proving for the person using the model. The hardware to do that is already in your pocket.
Notes
1. Fingerprint, analyzing 23 billion device identification events in 2025, found one in five web sessions arrived through a VPN, and one in three on desktop Chromium browsers. Surveys put it higher. In August 2026, 42% of US adults told Security.org they use a VPN, up from 32% a year earlier. Where access is restricted, VPN use is the norm: Iran's Parliament Research Center found 81% of Iranian internet users rely on a VPN. For Chinese users of US models, the transfer station does the VPN's job, so these figures understate the problem in those parts of the world. They may also leave out Apple's iCloud Private Relay and Cloudflare's WARP, both of which replace the user's IP address with one of their own. Private Relay comes with every paid iCloud plan. Apple has 2.5 billion active devices, and 64% of its US customers pay for iCloud storage (CIRP, 2024). Apple doesn't publish how many of them turn Private Relay on. Cloudflare's 1.1.1.1 app, which includes WARP, has more than 100 million downloads on Android alone.
References. Anthropic. "Detecting and countering misuse of AI: September 2026," 10 September 2026. Anthropic. "Detecting and preventing distillation attacks," 23 February 2026, anthropic.com. Cloudflare. "IP geolocation," Cloudflare documentation, developers.cloudflare.com. Fingerprint. "We Analyzed 23 Billion Device Identification Events," March 2026, fingerprint.com. Herbert Smith Freehills Kramer. "License to model: Emerging US rules impact global access to frontier AI," July 2026, hsfkramer.com. House Foreign Affairs Committee. H.R. 3447, Chip Security Act, ordered reported 42–0, 26 March 2026, foreignaffairs.house.gov. Iran International. "81% of Iranian internet users bypass censorship with VPNs," 24 February 2025, iranintl.com. ISPreview. "Ofcom Monitoring UK VPN Use Due to Circumvention of Online Safety Act," November 2025, ispreview.co.uk. Mayer Brown. "Commerce Department Extends Export Controls to Advanced AI Models," June 2026, mayerbrown.com. NASA Earth Observatory. "India-Pakistan Borderlands at Night," astronaut photograph ISS028-E-29679, 21 August 2011, science.nasa.gov. OFAC. "OFAC Settles with Binance Holdings, Ltd.," 21 November 2023, ofac.treasury.gov. OFAC. Settlement with Bittrex, Inc., 11 October 2022, ofac.treasury.gov. OFAC. Settlement with Payward, Inc. (Kraken), 28 November 2022, ofac.treasury.gov. OpenAI. Memo to the House Select Committee on Strategic Competition between the United States and the Chinese Communist Party, 12 February 2026, published by Bloomberg, assets.bwbx.io. Qian, Z. "How to Buy Cheap Claude Tokens in China," ChinaTalk, 5 May 2026, chinatalk.media. Security.org. "VPN Trends, Statistics, and Consumer Opinions," August 2026, security.org. Team Cymru. Fisher, S. "LLM Gateways: How They Enable Frontier Model Abuse," September 2026, team-cymru.com. UKTN. "Proton VPN reports surge in UK users after OSA," 6 August 2025, uktech.news.
Documentation. SDK documentation. Verifier source. Location Factor Authenticator.